// service · Advisory & Program
OT vulnerability management without a patching fantasy
Rank OT vulnerabilities by plant consequence, not CVSS. Compensating controls and change windows. A program your plants can run this year.
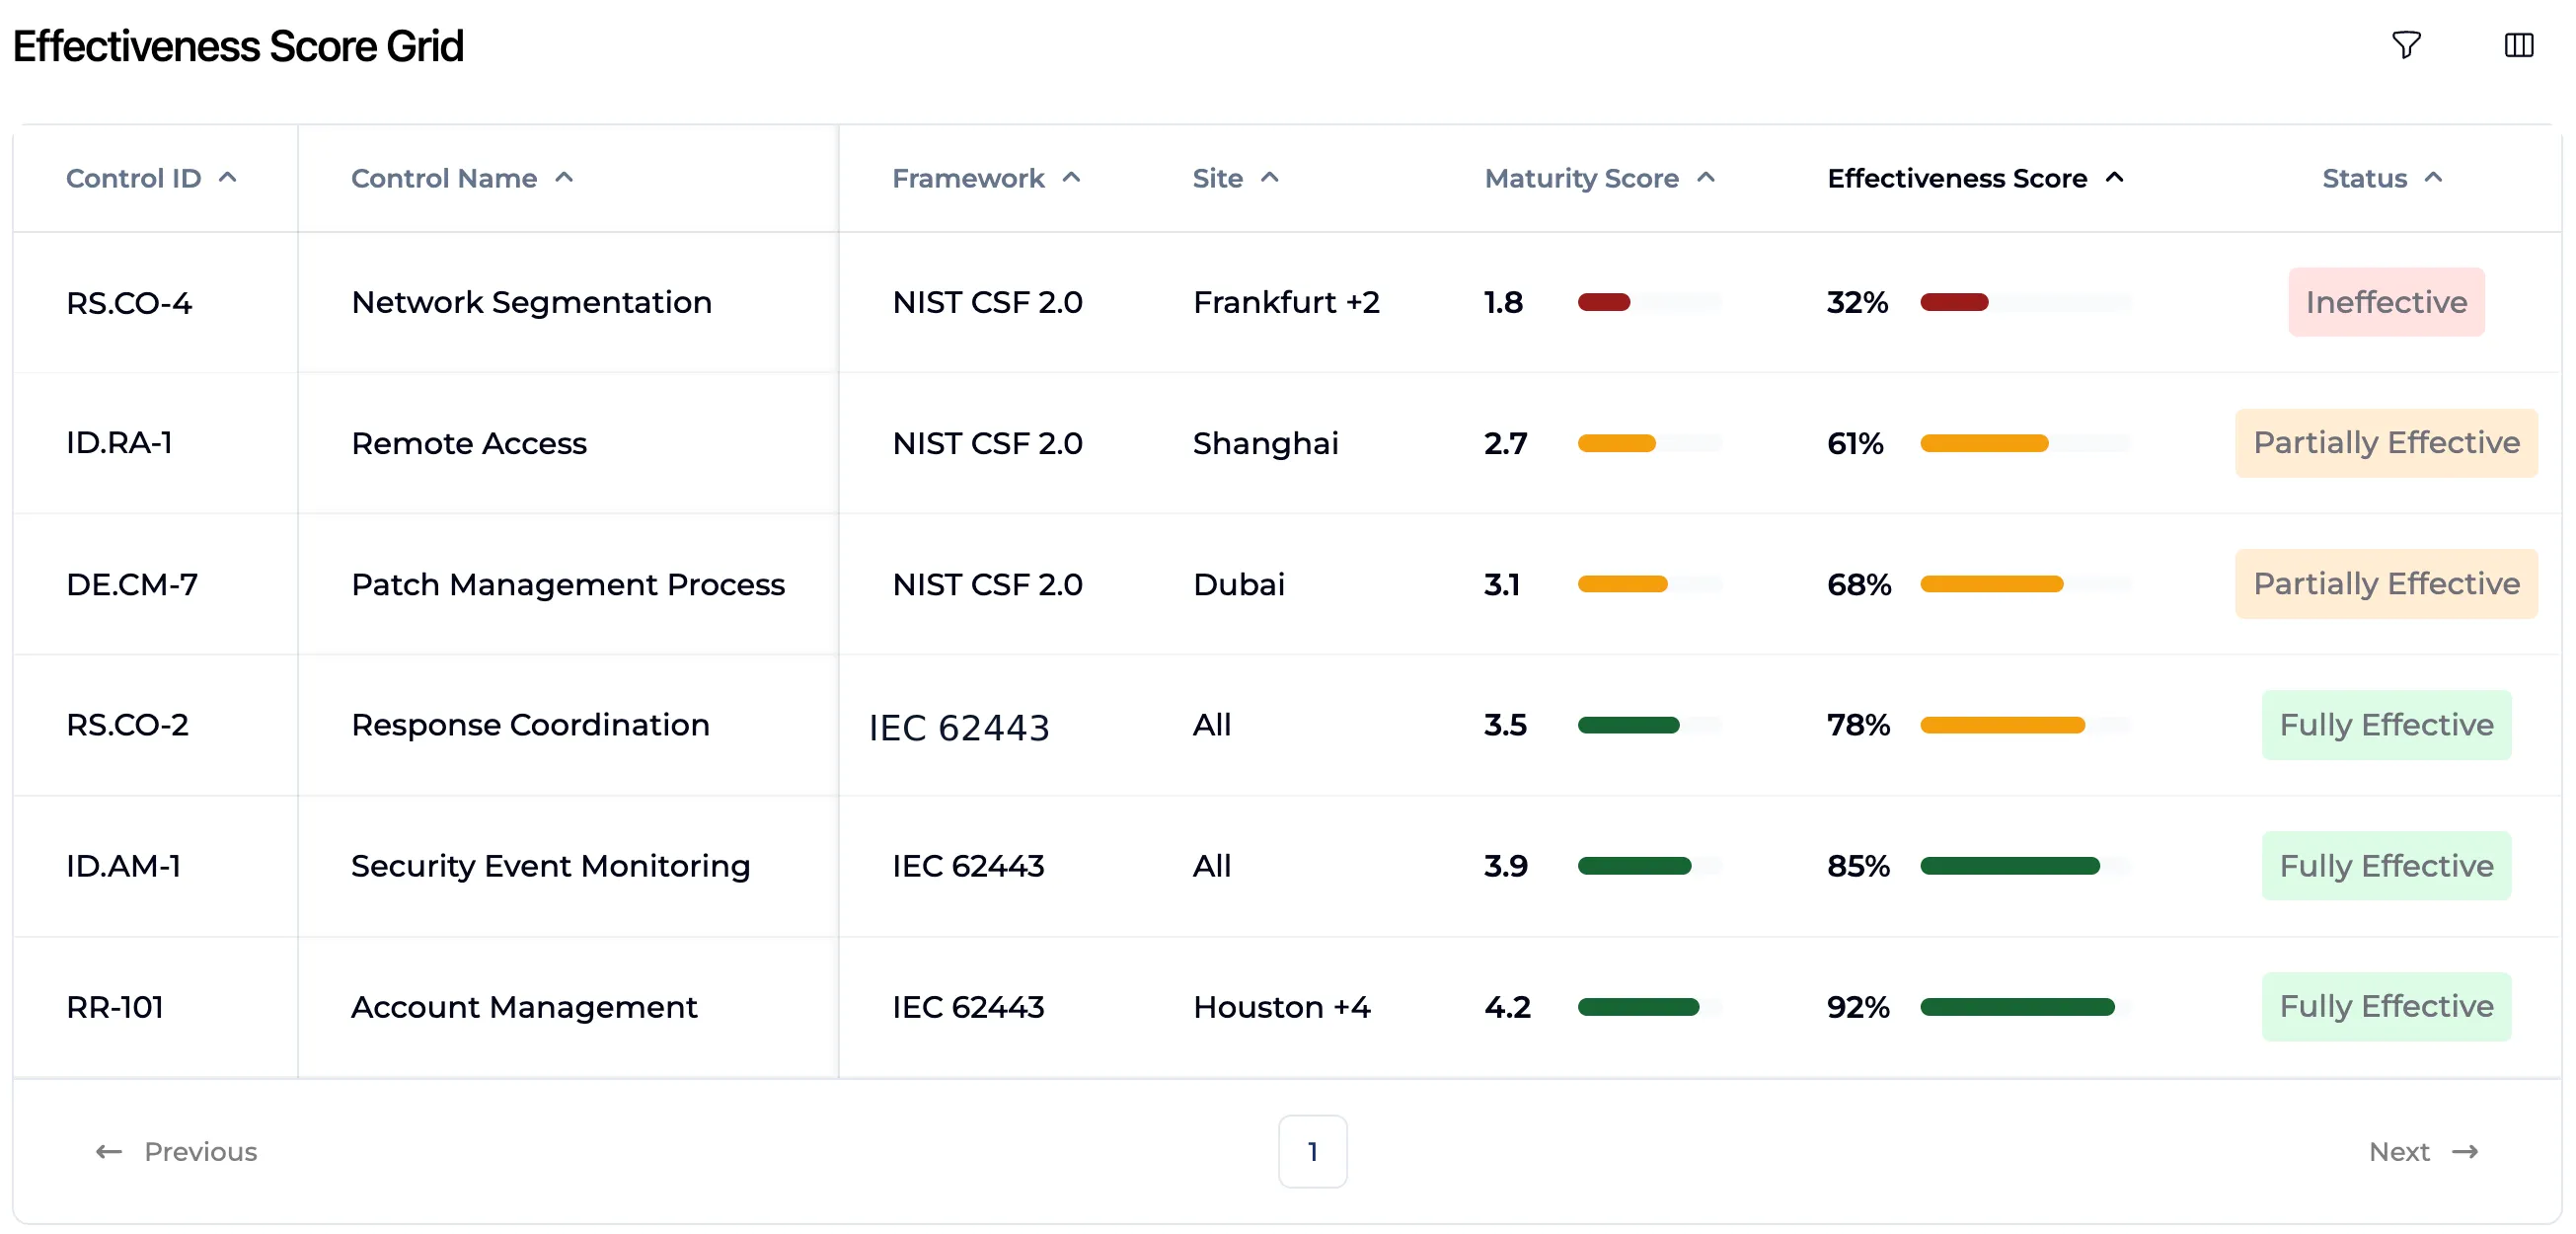
Most OT vulnerability programs got copied from IT and bolted on. The scanner runs across the IDMZ once a quarter and produces a thousand-line spreadsheet. Plants ignore it because patching a PLC at 0200 is not a thing, and the CVSS-9 list sits on the CISO’s desk while the real exposure goes untouched.
This service builds a program the plant can live with. We prioritize by production impact and exploitability in context, define compensating controls where patching is not an option, and set a remediation cadence operations will actually run.
You get vulnerability management that reduces risk instead of generating reports, with every item tracked to closure in Resilion.
// FAQ
Questions about OT vulnerability management program
- How does OT vulnerability management differ from IT?
- You often cannot patch a PLC at 0200, so a CVSS-ranked spreadsheet is useless. An OT program prioritizes by production impact and exploitability in context, leans on compensating controls when patching is not feasible, and runs on a cadence operations can actually sustain.
- What do you build?
- The full program: asset and vulnerability sources, a prioritization model tied to plant impact, compensating-control playbooks, and a closure cadence, wired into Resilion so remediation is tracked, not lost in a spreadsheet.
See this work on your sites
Book a 30-minute demo. Bring the last assessment and the sites in the first wave.